
Architecture
How ntwire works
ntwire is a userspace WireGuard multi-tunnel service. A client authenticates to a server, receives only the tunnel grants it is allowed to use, then sends permitted traffic through encrypted transport.
A direct connection
The client authenticates with an SSH key or OIDC. The server grants only configured targets; the client opens local listeners for them.
Control-plane requests are protected with TLS. The data plane uses WireGuard; when UDP is unavailable, ntwire can use an authenticated WebSocket transport. Transport selection should not change which grants apply.
When the server is behind NAT
The relay does not terminate the client’s TLS or WireGuard session. It forwards opaque traffic to a registered server.
ntwire-gui processes
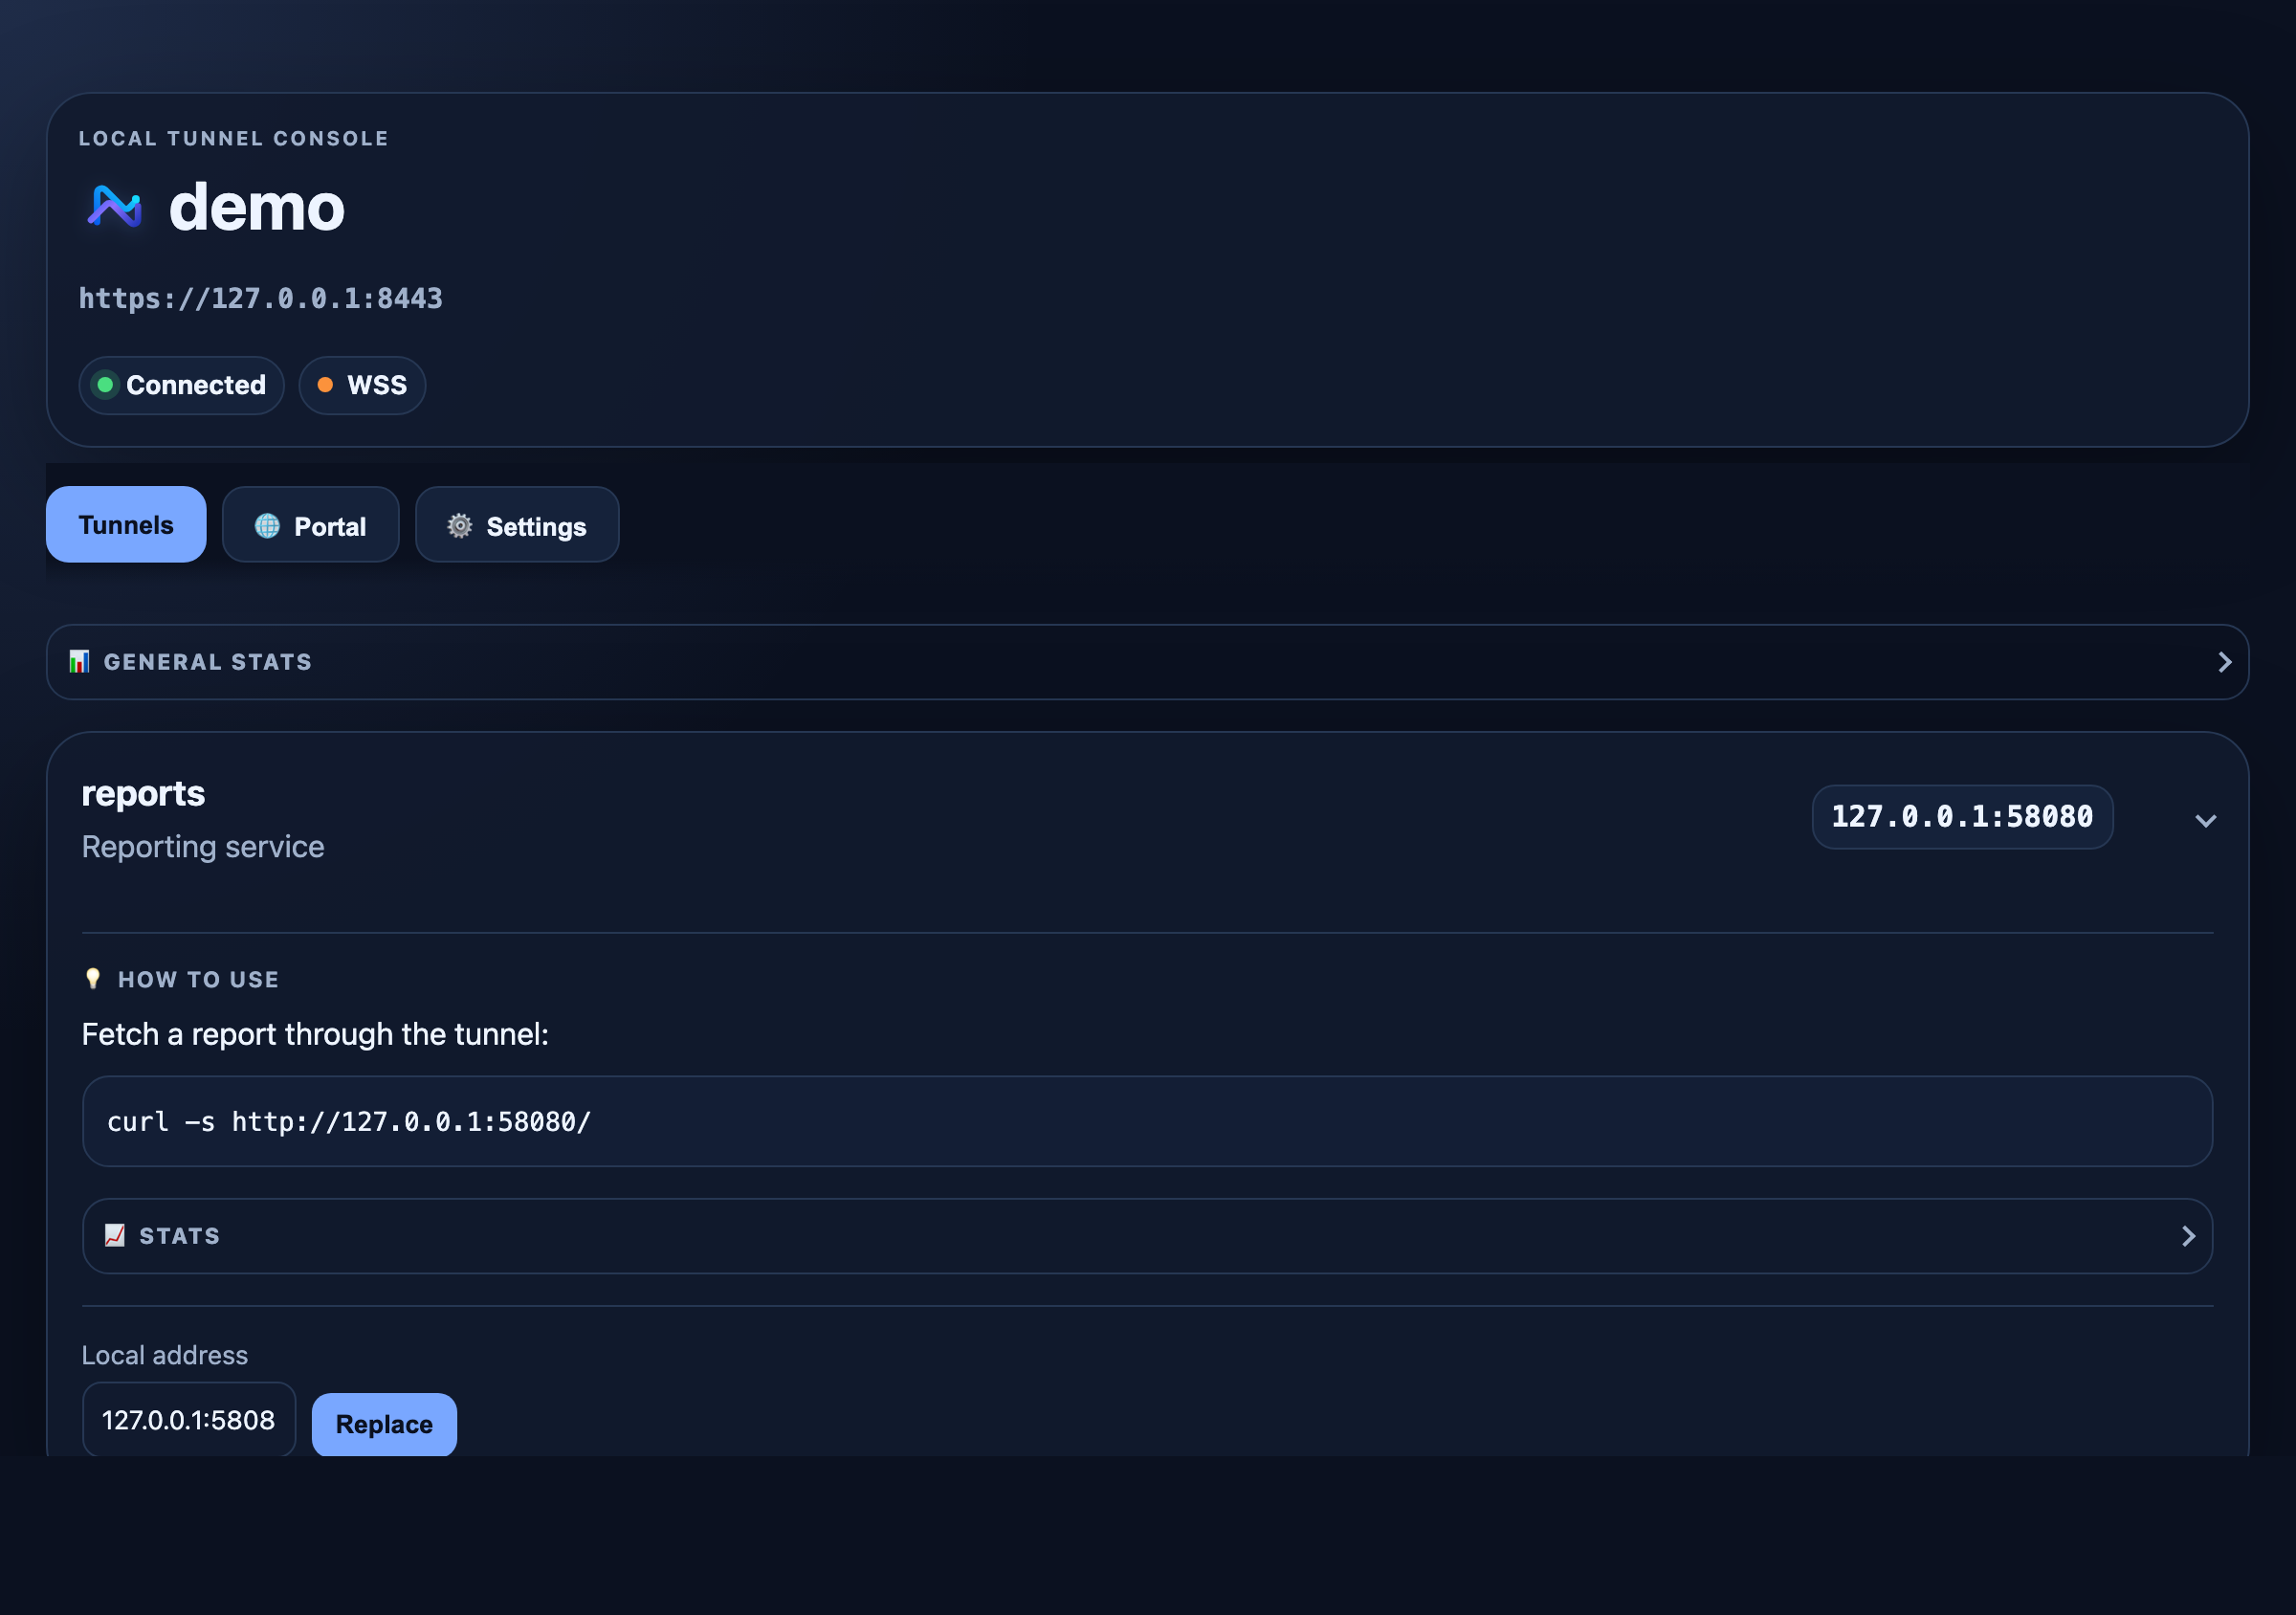
The tray process remains independent of the settings window. Closing the settings window does not disconnect tunnels; its settings UI is an authenticated client of the local API.
For configuration matrices and every client/server combination, see the canonical Connecting guide and GUI guide.